Wellington IT Breach Exposes Saved Payee Data Across Irish Credit Unions
Wellington IT Breach Exposes Saved Payee Data Across Irish Credit Unions
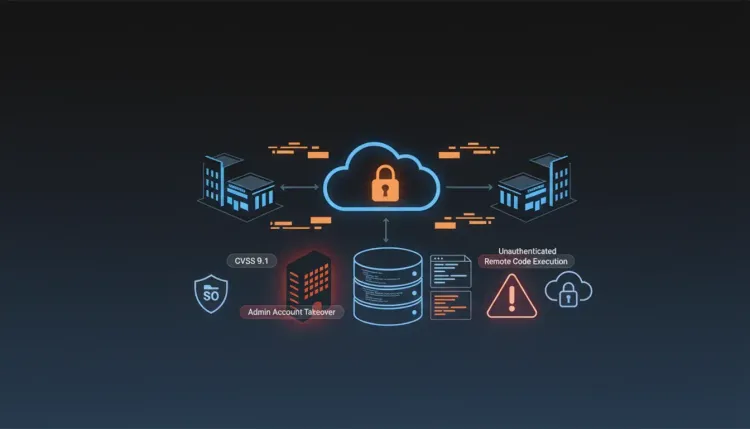
An authorization flaw in Wellington IT's CU Online platform exposed saved payee records linked to customers of dozens of Irish credit unions. The incident is a warning that a breach at a shared financial-services provider can turn one application weakness into a sector-wide notification and fraud risk.
What happened
Wellington IT provides transaction-processing and online-banking services to credit unions in Ireland. According to RTÉ and reporting by Recorded Future News, attackers exploited a vulnerability in the provider's systems and retrieved information associated with saved payees. Around 40 credit unions have reported the incident to Ireland's Data Protection Commission, while the exact number of affected people remains under investigation.
The exposed fields may include a payee's name, nickname, IBAN, BIC, account number, sort code, address, and payment-reference information. Those details can reveal who a member pays and provide useful context for impersonation or targeted fraud.
The incident should be understood as a data breach, even though current public statements say there is no evidence that members' account passwords, PINs, balances, or funds were accessed. Data that does not move money directly can still make a convincing phishing message easier to write.
Why the supplier relationship matters
This was not an isolated compromise of one credit union's front end. A common service provider created a concentration point: one authorization failure could expose records across many institutions. That is a practical access control lesson for every organization that shares a platform, processor, or managed service.
Public reporting says the attack activity occurred in early October, the vulnerability was closed shortly afterward, and credit unions were informed in mid-November after a later review identified the potential data-protection impact. Wellington IT says it has engaged external cybersecurity specialists and is cooperating with the Data Protection Commission, the National Cyber Security Centre, and law enforcement.
For regulated organizations, supplier assurance cannot stop at a contract and an annual questionnaire. Customers need evidence that providers can enforce tenant isolation, log object-level access, detect abnormal request volumes, preserve forensic evidence, and notify downstream organizations quickly when the scope changes.
Defensive priorities
Credit unions and other financial institutions using shared providers should:
- Confirm exactly which datasets and tenants were reachable during the attack window.
- Preserve application, API gateway, identity, and database logs before retention policies overwrite them.
- Review authorization tests for horizontal access between members, payees, and tenants.
- Notify potentially affected people with specific guidance, while warning them never to share passwords, PINs, or one-time codes.
- Hunt for follow-on social engineering using exposed payee relationships, references, and payment context.
- Reassess supplier incident-notification terms, monitoring access, and independent testing requirements.
The lesson
The immediate exposure appears limited to saved payee information, but the trust impact is wider. Shared providers must be treated as part of the financial institution's attack surface, and authorization telemetry must be good enough to answer not only whether a flaw was fixed, but whose records may have been touched before it was fixed.
Sources
- RTÉ: Credit union users alerted as soon as potential risk identified
- RTÉ: Initial investigation did not identify credit union breach
- Recorded Future News: Dozens of credit unions hit by supplier breach
- The Journal: Credit unions seek answers on scale of data breach
References
FAQ
An authorization flaw in Wellington IT's CU Online platform exposed saved payee records linked to customers of dozens of Irish credit unions. The incident is a warning that a breach at a shared financial-services provider can turn one application weakness into a sector-wide notification and fraud risk.
This was not an isolated compromise of one credit union's front end. A common service provider created a concentration point: one authorization failure could expose records across many institutions. That is a practical access control lesson for every organization that shares a platform, processor, or managed service.