Barracuda ESG Flaws Chain to Root Access: Why the Admin UI Is Now a Critical Boundary
Barracuda ESG Flaws Chain to Root Access: Why the Admin UI Is Now a Critical Boundary
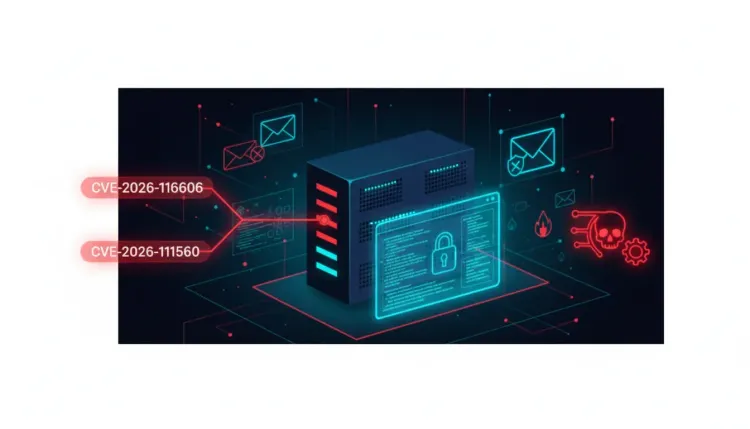
Barracuda has disclosed two vulnerabilities that can be chained to take over affected security appliances with root privileges. The most serious issue, CVE-2026-116606, is a pre-authentication authorization bypass in Email Security Gateway (ESG). The second, CVE-2026-111560, is a command-injection flaw affecting ESG and several other Barracuda products.
The practical risk is larger than either CVE in isolation. An attacker who can reach the administrative interface may use the first flaw to alter global configuration and then combine it with the second to execute operating-system commands as root. A device intended to protect email or web traffic can therefore become a privileged foothold inside the network.
What Barracuda confirmed
Barracuda rates CVE-2026-116606 at CVSS 9.3 and CVE-2026-111560 at CVSS 8.6. The vendor says exploitation requires access to the product's administrative UI, but authentication is not required for the authorization-bypass path. That distinction matters: an admin interface can be private from the public internet and still be exposed through a compromised VPN account, a flat management network, or an attacker who has already obtained an internal foothold.
The two vulnerabilities affect products differently. Email Security Gateway is affected by both. Load Balancer ADC, Message Archiver, WAF Control Center, Web Application Firewall, and Web Security Gateway are affected by CVE-2026-111560. Barracuda released product-specific fixes and recommends checking that automatic patching is enabled and that devices are running the latest firmware.
Why chaining changes the response
An authentication bypass is dangerous because it removes an identity check from a privileged path. A command injection is dangerous because attacker-controlled input can cross from an application feature into the operating system. Chained together, the flaws turn configuration access into privilege escalation and potentially full appliance compromise.
This is also an attack surface problem. Security appliances are often trusted by default, placed in sensitive network segments, and excluded from ordinary endpoint monitoring. If attackers gain root on the appliance, they may be able to inspect configurations, alter routing or filtering behavior, harvest secrets, or use the device for lateral movement.
The right question is not only whether the management page is internet-facing. Defenders should map every route to it: remote-access gateways, jump hosts, administrator workstations, vendor support paths, and service accounts. A management interface that is technically internal can still be reachable through a compromised identity or over-permissive network path.
Defensive actions for Barracuda customers
- Apply Barracuda's current firmware and product-specific fixes for CVE-2026-116606 and CVE-2026-111560. Treat patch management as an incident-response priority, not a routine maintenance item.
- Restrict administrative interfaces to trusted management networks. Do not expose them directly to the internet; require a hardened jump host or equivalent controlled access path.
- Review administrator accounts, recent logins, configuration imports, timezone changes, firmware events, and unexpected changes to filtering or routing rules.
- Hunt for new local users, modified startup tasks, unusual outbound connections, unexpected shell activity, and changes made outside approved maintenance windows.
- Rotate credentials and tokens used by the appliance if compromise is suspected. Review adjacent systems that trusted the device or shared management credentials.
- Preserve logs and configuration snapshots before making disruptive changes. Engage incident response support if there is evidence of unauthorized configuration or command execution.
- Segment management traffic and enforce least privilege so a compromised appliance cannot become a bridge to core identity, mail, or administration systems.
The broader lesson
Security appliances deserve the same exposure management as internet-facing application servers. Their protective role does not make their management plane safe; it makes compromise more consequential. The Barracuda chain shows how a reachable administrative interface, an authorization weakness, and an OS command path can collapse multiple trust boundaries at once.
Organizations should inventory every security appliance, verify its management exposure, and test whether its logs would reveal a configuration-abuse chain. Patching closes the immediate vulnerability, but isolating management access and reducing the appliance's standing trust determine how far an attacker can go after the next flaw is found.
References
FAQ
Barracuda has disclosed two vulnerabilities that can be chained to take over affected security appliances with root privileges. The most serious issue, CVE-2026-116606, is a pre-authentication authorization bypass in Email Security Gateway (ESG). The second, CVE-2026-111560, is a command-injection flaw affecting ESG and several other Barracuda products.
An authentication bypass is dangerous because it removes an identity check from a privileged path. A command injection is dangerous because attacker-controlled input can cross from an application feature into the operating system. Chained together, the flaws turn configuration access into privilege escalation and potentially full appliance compromise.